Thursday, 18 January 2024

October 2019 Connector

OWASP
Connector
October 2019

COMMUNICATIONS


Letter from the Vice Chairman of the Board

Dear OWASP Community,  

Two of the primary initiatives the foundation staff has been working on over the past few months were the two back to back Global AppSec Events in DC and Amsterdam.  This was a huge undertaking by everyone involved.  We are pleased to announce that the survey feed back is positive and both events were well attended.  I was in attendance of Global AppSec Amsterdam and it was great meeting and speaking with old friends and meeting new ones.  I would also like to take this opportunity, on behalf of the board to thank OWASP staff for their efforts in making the two conferences so successful. 

To continuing on with the events theme; I'm really happy to announce the locations of our 2020 OWASP Global AppSec Conferences.  The first one will be June 15 - 19, 2020 in Dublin and the second will be October 19 - 23, 2020 in San Francisco.  Dublin is not an exotic trip for me, more of a 10 minute tram ride.  Hopefully you will join us, while also making the most of the culture and scenery that Ireland has to offer.   

Last but not least, the OWASP Global Board of Directors election results where released Thursday October 17, 2019. I'd like to first thank everyone who has put their trust in me by voting me back onto the board for the next two years. I hope I do you justice.

I would also like to thank the large number of candidates that were willing to give of their personal time and run to be part of the Global OWASP Board.  This is a testament of the dedication and commitment of our members to continue to grow and evolve to the next level as an organization.  I encourage those that were not elected will still be involved in making a positive change by volunteering to be part of a committee.  The board and staff need all the help they can get to push through change. I hope you will join us in this journey.  We can not be successful without the help of the community. 

Until next time, 
Owen Pendlebury 
Vice Chairman, OWASP Global Board of Directors 
OWASP Global Board Election Results 
 
The newly elected 2020 OWASP Board Members:
Grant Ongers
Owen Pendlebury
Sherif Mansour
Vandana Verma Sengal
 
Congratulations, and thank you to all the candidates that participated and the OWASP members that voted. 
OWASP Foundation Global AppSec Event Dates for 2020

Global AppSec Dublin, June 15 - 19, 2020

Global AppSec San Francisco, October 19 - 23, 2020


Visit our website for future announcements.

EVENTS 

You may also be interested in one of our other affiliated events:


REGIONAL EVENTS
Event Date Location
BASC 2019 (Boston Application Security Conference) October 19,2019 Burlington, MA
LASCON X October 24 - 25, 2019 Austin, TX
OWASP AppSec Day 2019 Oct 30 - Nov 1, 2019 Melbourne, Australia
German OWASP Day 2019 December 9 - 10, 2019 Karlsruhe, Germany
AppSec California 2020 January 21 - 24, 2020 Santa Monica, CA
OWASP New Zealand Day 2020 February 20 - 21, 2020 Auckland, New Zealand
Seasides 2020 March 3 - 5, 2020 Panjim Goa, India
SnowFROC 2020 March 5, 2020 Denver, CO

GLOBAL PARTNERSHIP EVENTS
Event Date Location
BlackHat Europe 2019 December 2 - 5, 2019 London


BlackHat Europe 2019 London at EXCEL London
2019 December 2-5 
Visit the OWASP Booth 1015
Business Hall December 4 & 5 
December 4, 10:30 AM - 7:00 PM
December 5: 10:00 AM - 4:00 PM

OWASP Members are eligible for € 200.00 discount , email marketing@owasp.org for code to use when registering.

PROJECTS

Projects were well-represented at the previous two Global AppSec conferences in DC and Amsterdam this past month.  Both events featured the popular Project Showcase and I heartily thank the leaders of the projects who participated:

Secure Medical Device Deployment Standard
Secure Coding Dojo
API Security Project
Dependency Check
SAMM
SEDATED
DefectDojo
Juice Shop
ModSecuity Core Rule Set
SecurityRAT
WebGoat

These leaders put on a great set of presentations and, in many cases, the room was standing room only.  Thank you!

The project reviews that were done in DC and Amsterdam are still being evaluated and worked on; if you are waiting on answers, please have patience.  I hope to have them finalized by November.

The website migration continues moving forward.  The process of adding users to the proper repositories is an on-going effort.  If you have not given your GitHub username, please drop by the Request for Leader Github Usernames form.  A nice-to-accomplish goal would be to have the projects and chapters in their new website homes within the next 30 days.

Harold L. Blankenship
Director of Technology and Projects

COMMUNITY

Welcome to the New OWASP Chapters 
Sacramento, California
Marquette, Michigan
Ranchi, India
Paraiba, Brazil
Calgary, Canada 

CORPORATE MEMBERS 

 
Premier Corporate Member
Contributor Corporate Members

*Ads and logos are not endorsements and reflect the messages of the advertiser only. *
Join us
Donate
Our mailing address is:
OWASP Foundation 
1200-C Agora Drive, #232
Bel Air, MD 21014  
Contact Us
Unsubscribe


This email was sent to *|EMAIL|*
why did I get this?    unsubscribe from this list    update subscription preferences
*|LIST:ADDRESSLINE|*

Hackerhubb.blogspot.com

Hackerhubb.blogspot.com

Related word


Wednesday, 17 January 2024

Reversing Pascal String Object

There are many goodware and malware developed in pascal, and we will see that the binary generated by the pascal compilers is fascinating, not only because the small and clean generated binaries, or the  clarity of the pascal code, but also the good performance. In Linux we have Lazarus which is a good free IDE like Delphi and Kylix the free pascal IDE for windows.

The program:

program strtest;

var
  cstr:  array[0..10] of char;
  s, s2:  ShortString;

begin
  cstr := 'hello world';
  s  := cstr;
  s2 := 'test';
  
  WriteLn(cstr + ' ' + s + ' ' + s2);
end.


We are going to compile it with freepascal and lazarus, and just the binary size differs a lot:

lazarus          242,176 btytes  845 functions
freepascal       32,256 bytes   233 functions
turbopascal      2,928 bytes     80 functions  (wow)

And surprisingly turbopascal binaries are extremely light.
Lets start with lazarus:


Logically it imports from user32.dll some display functions, it also import the kernel32.dll functions and suspiciously the string operations of oleaut32.dll 


And our starting point is a function called entry that calls the console initialization and retrieve some console configurations, and then start a labyrinth of function calls.


On functions 10000e8e0 there is the function that calls the main function.

I named execute_param2 because the second param is a function pointer that is gonna be executed without parameters, it sounds like main calling typical strategy.
And here we are, it's clearly the user code pascal main function.


What it seems is that function 100001800 returns an string object, then is called its constructor to initialize the string, then the string is passed to other functions that prints it to the screen.

This function executes the method 0x1c0 of the object until the byte 0x89 is a null byte.
What the hell is doing here?
First of all let's create the function main:


Simply right button create function:

After a bit of work on Ghidra here we have the main:


Note that the struct member so high like 0x1b0 are not created by default, we should import a .h file with an struct or class definition, and locate the constructor just on that position.

The mysterious function was printing byte a byte until null byte, the algorithm the compiler implemented in asm is not as optimized as turbopascal's.

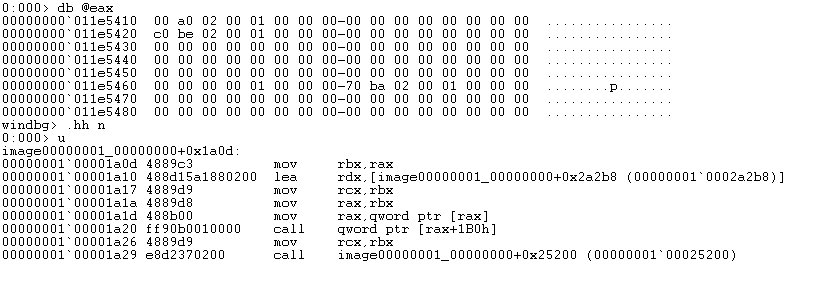
In Windbg we can see the string object in eax after being created but before being initialized:


Just before executing the print function, the RCX parameter is the string object and it still identical:


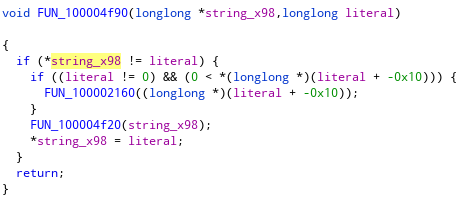
Let's see the constructor code.
The constructor address can be guessed on static walking the reverse-cross-references to main, but I located it in debugging it in dynamic analysis.


The constructor reads only a pointer stored on the string object on the position 0x98.

And we have that the pointer at 0x98 is compared with the address of the literal, so now we know that this pointer points to the string.
The sentence *string_x98 = literal confirms it, and there is not memory copy, it only points reusing the literal.


Freepascal

The starting labyrinth is bigger than Lazarus so I had to begin the maze from the end, searching the string "hello world" and then finding the string references:


There are two ways to follow the references in Ghidra, one is [ctrl] + [shift] + F  but there is other trick which is simply clicking the green references texts on the disassembly.

At the beginning I doubted and put the name possible_main, but it's clearly the pascal user code main function.


The char array initialization Is converted by freepascal compiler to an runtime initialization using mov instructions.

Reducing the coverage on dynamic we arrive to the writeln function:


EAX helds  a pointer to a struct, and the member 0x24 performs the printing. In this cases the function can be tracked easily in dynamic executing the sample.

And lands at 0x004059b0 where we see the WriteFile, the stdout descriptor, the text and the size supplied by parameter.


there is an interesting logic of what happens if WriteFile() couldn't write all the bytes, but this is other scope.
Lets see how this functions is called  and how text and size are supplied to figure out the string object.


EBX helds the string object and there are two pointers, a pointer to the string on 0x18 and the length in 0x18, lets verify it on windbg.


And here we have the string object, 0x0000001e is the length, and 0x001de8a68 is the pointer.


Thanks @capi_x for the pascal samples.

Related articles


  1. Hack Tool Apk No Root
  2. Pentest Reporting Tools
  3. Hacking Tools Pc
  4. Hacking Tools Github
  5. Hacking Tools Kit
  6. Hack Tools Download
  7. Hacker Tools For Windows
  8. Wifi Hacker Tools For Windows
  9. How To Hack
  10. Hacker Tools For Windows
  11. Hack Rom Tools
  12. Hack Tools For Games
  13. Hacking Tools Online
  14. Nsa Hack Tools
  15. Underground Hacker Sites
  16. Hacker Tools Windows
  17. Hack Tools Github
  18. Physical Pentest Tools
  19. Hack Tools Github
  20. Hacker
  21. World No 1 Hacker Software
  22. Hacker Tools Windows
  23. Hacker Tools For Mac
  24. Hacking Tools Software
  25. Hack And Tools
  26. Pentest Tools Kali Linux
  27. Nsa Hacker Tools
  28. Hack Website Online Tool
  29. Hacker Tools Free
  30. Hacker Security Tools
  31. Pentest Tools Android
  32. Hacker Security Tools
  33. Hacker Tools For Ios
  34. Pentest Tools Website
  35. Hacking Tools 2019
  36. Pentest Automation Tools
  37. Pentest Tools Tcp Port Scanner
  38. Best Hacking Tools 2019
  39. Hacker Tools Free
  40. Hack Tools For Ubuntu
  41. Hack Tools Pc
  42. Hacking Tools And Software
  43. Hack Tools For Windows
  44. Github Hacking Tools
  45. Hacking Tools Free Download
  46. Hacker Security Tools
  47. Hacker Tools Free Download
  48. Hacking Tools For Windows Free Download
  49. Hacker Tools Software
  50. Hacker Tools 2020
  51. Hacker Tools For Mac
  52. Hacking Tools Pc
  53. Hacking Tools
  54. Hacker Tools Github
  55. Nsa Hacker Tools
  56. Pentest Recon Tools
  57. Underground Hacker Sites
  58. Pentest Tools For Windows
  59. Tools Used For Hacking
  60. Hacking Tools For Pc
  61. Hacking Tools Pc
  62. Hacker Tools For Pc
  63. Hacker Tools Apk Download
  64. Hack Tools Github
  65. Pentest Tools Windows
  66. Tools 4 Hack
  67. Pentest Tools Framework
  68. Pentest Tools Free
  69. Hacker Tools Free Download
  70. Tools Used For Hacking
  71. Hacker Tools List
  72. Hacker Tools Software
  73. Hacker Tools Linux
  74. Hacker Tools Software
  75. Hacking Tools Mac
  76. Bluetooth Hacking Tools Kali
  77. Hack App
  78. Pentest Tools Framework

HACK SNAPCHAT ACCOUNT BY MAC SPOOFING

In the last article, I have discussed a method on how to hack SnapChat account using SpyStealth Premium App. In this article, I am gonna show you an advanced method that how to hack SnapChat account by mac spoofing. It works same as WhatsApp hacking by mac spoofing. It's a bit more complicated than the last method discussed and requires proper attention. It involves the spoofing of the mac address of the target device. Let's move on how to perform the attack.

HOW TO HACK SNAPCHAT ACCOUNT BY MAC SPOOFING?

Note: This method will work if SnapChat is created on a phone number.
Here I will show you complete tutorial step by step of hacking the SnapChat account. Just understand each step carefully.
  1. Find out the victim's phone and note down it's Mac address. To get the mac address in Android devices, go to Settings > About Phone > Status > Wifi Mac address. And here you'll see the mac address. Just write it somewhere. We'll use it in the upcoming steps.
  2. As you get the target's mac address, you have to change your phone's mac address with the target's mac address. Perform the steps mentioned in this article on how to spoof mac address in android phones.
  3. Now install SnapChat on your phone and use victim's number while you're creating an account. It'll send a verification code to victim's phone. Just grab the code and enter it here.
  4. Once you do that, it'll set all and you'll get all chats and messages which victims sends or receives.
This method is really a good one but very difficult for the non-technical users. Only use this method if you're technical skills and have time to perform every step carefully. Otherwise, you can hack SnapChat account using Spying app.
Related articles